


SignalFisher at GISEC Global 2026: Building Confidence Through Intelligent Security Testing
3 min. reading time – Three days in Dubai reinforced a clear message: Security testing must evolve on a continuous basis. AI is accelerating change, attack surfaces are expanding, and the occasional snapshot is no longer enough. Organizations need intelligent security testing programs that remain relevant, current, and trusted.
Dubai, UAE - GISEC Global 2026 once again brought together cybersecurity leaders, innovators, and decision makers from across the Middle East and around the globe. For SignalFisher, the event was more than an opportunity to showcase its approach to security testing. It was a chance to engage in meaningful conversations about one of the most pressing challenges facing organizations today: How to maintain confidence in an ever-changing threat landscape.
Over three inspiring days in Dubai, the team met with CISOs, security leaders, partners, and practitioners who all share a common concern. AI is accelerating change, attack surfaces continue to expand, and traditional security testing approaches are struggling to keep pace. The conversations confirmed what we strongly believe at SignalFisher: Cyber security can no longer rely on scheduled snapshots. Security testing must become continuous, adaptive, and relevant to current business risk.
From periodic testing to an intelligent testing program
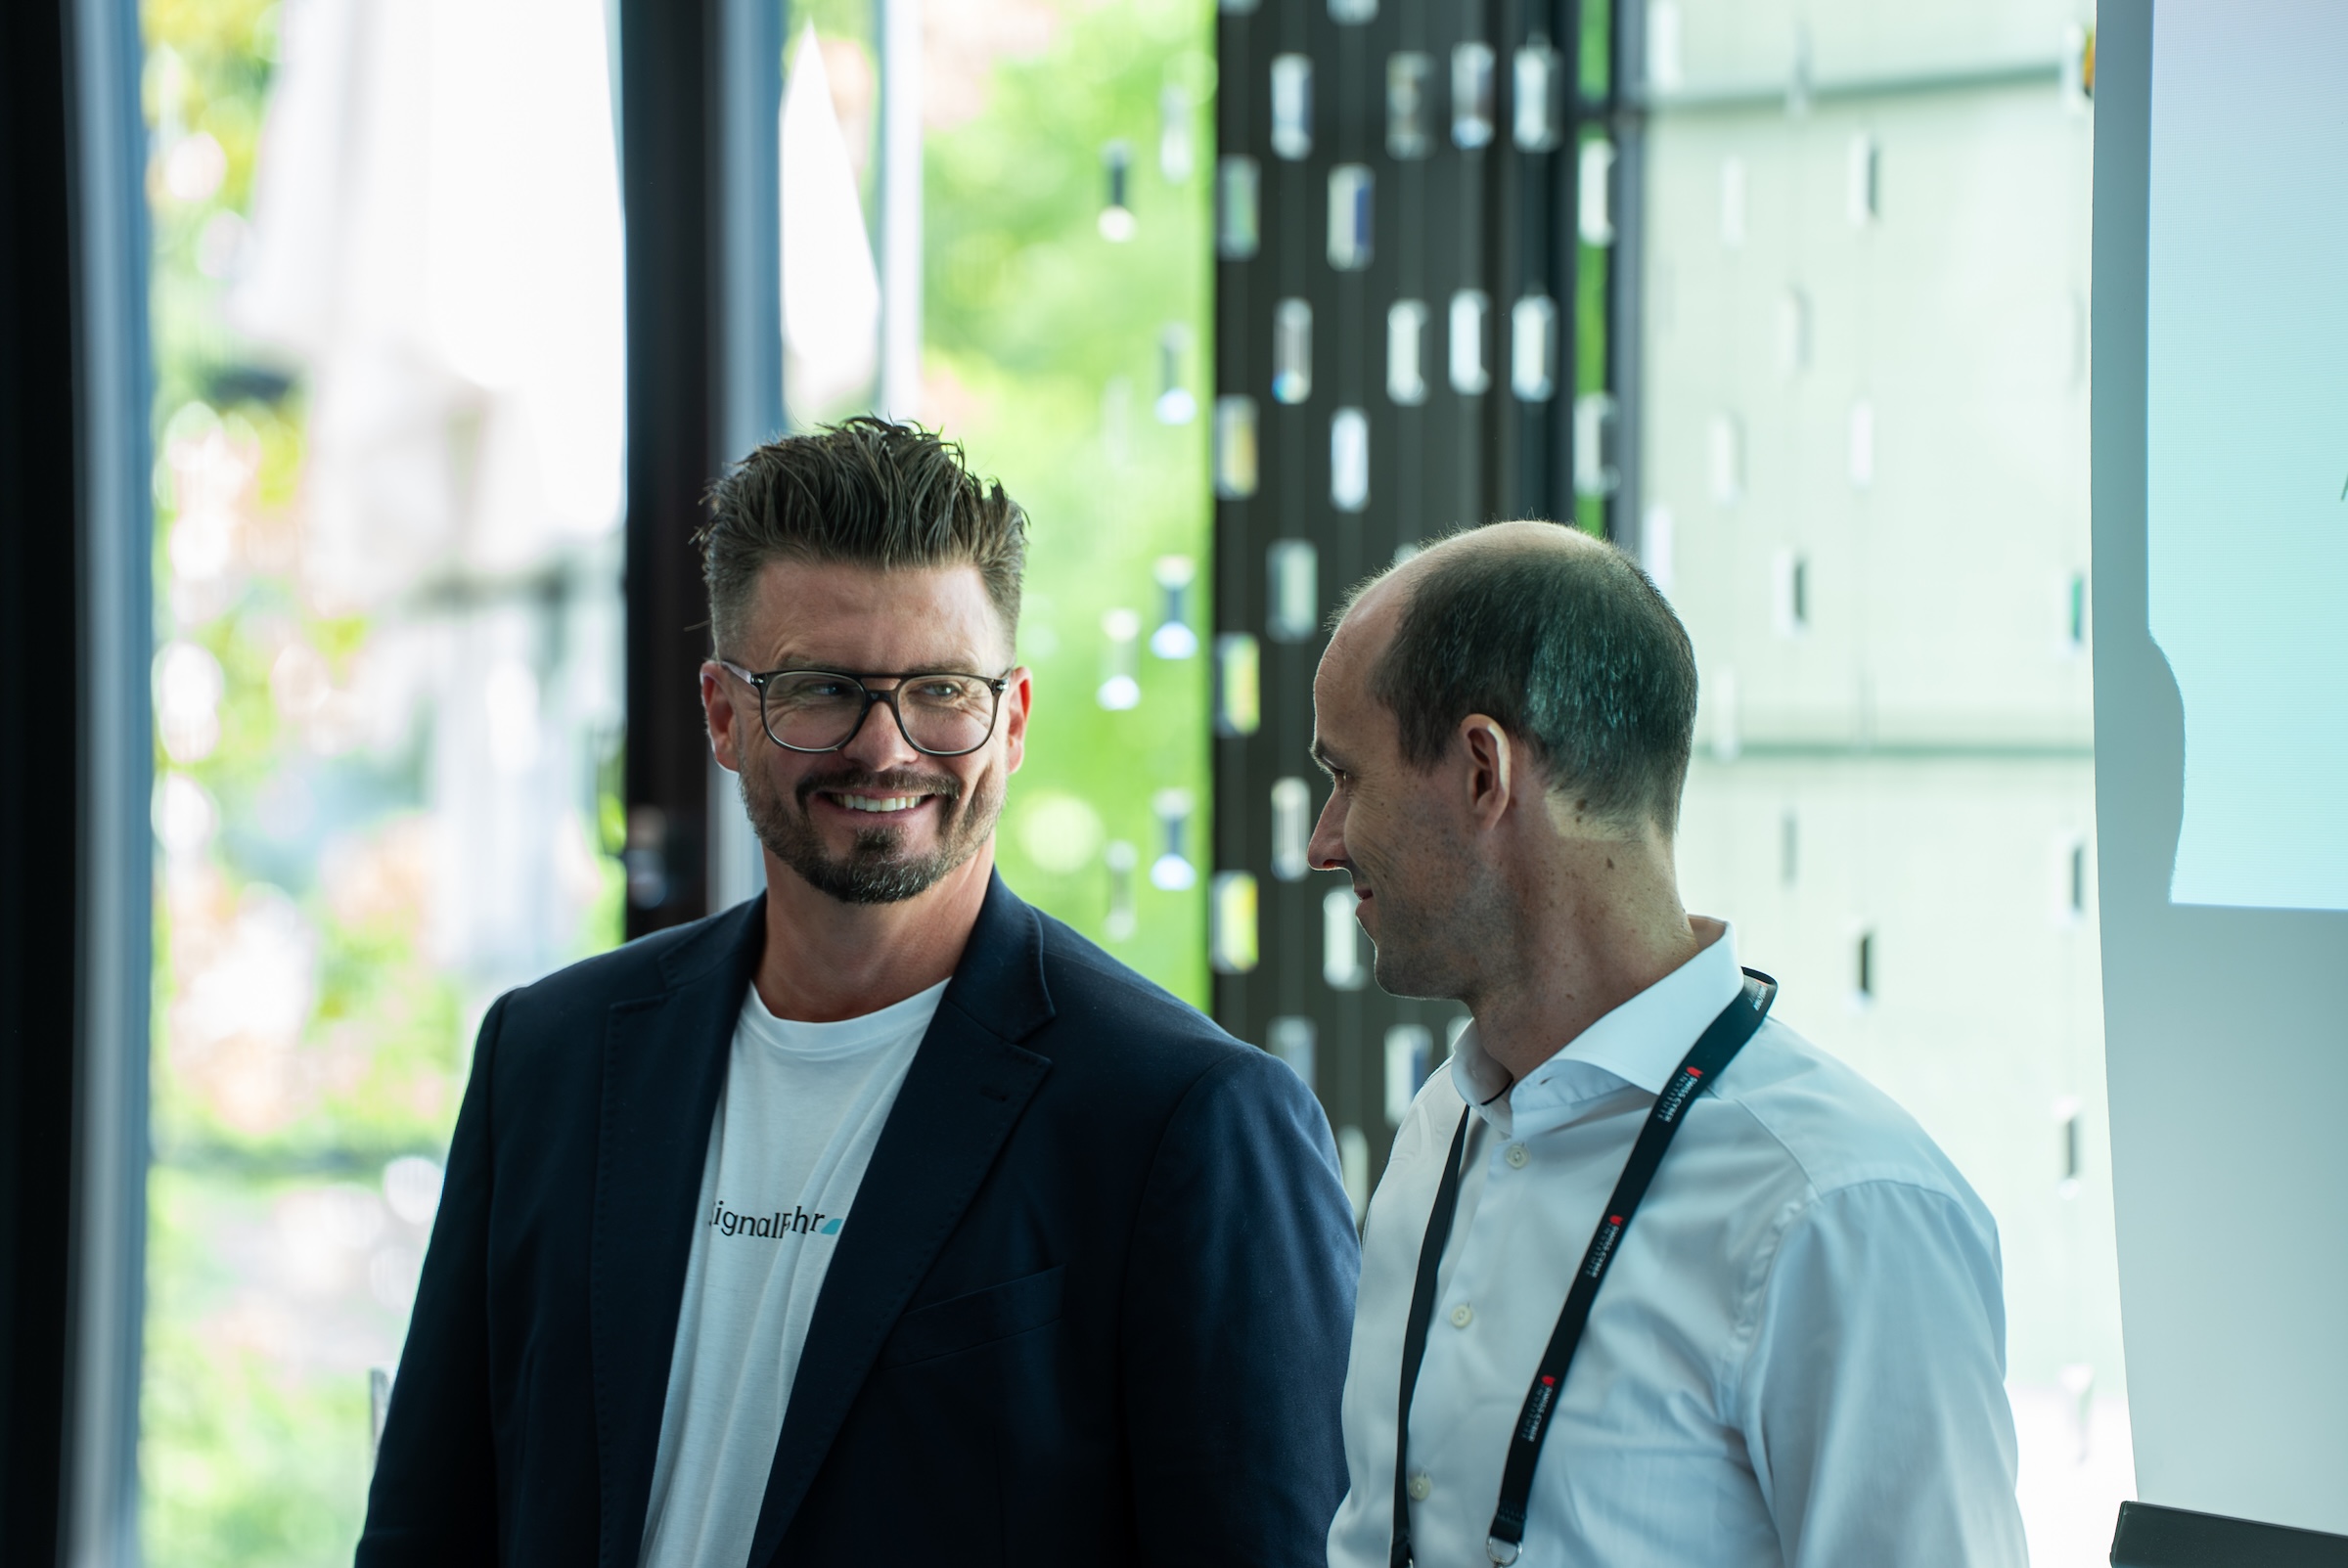
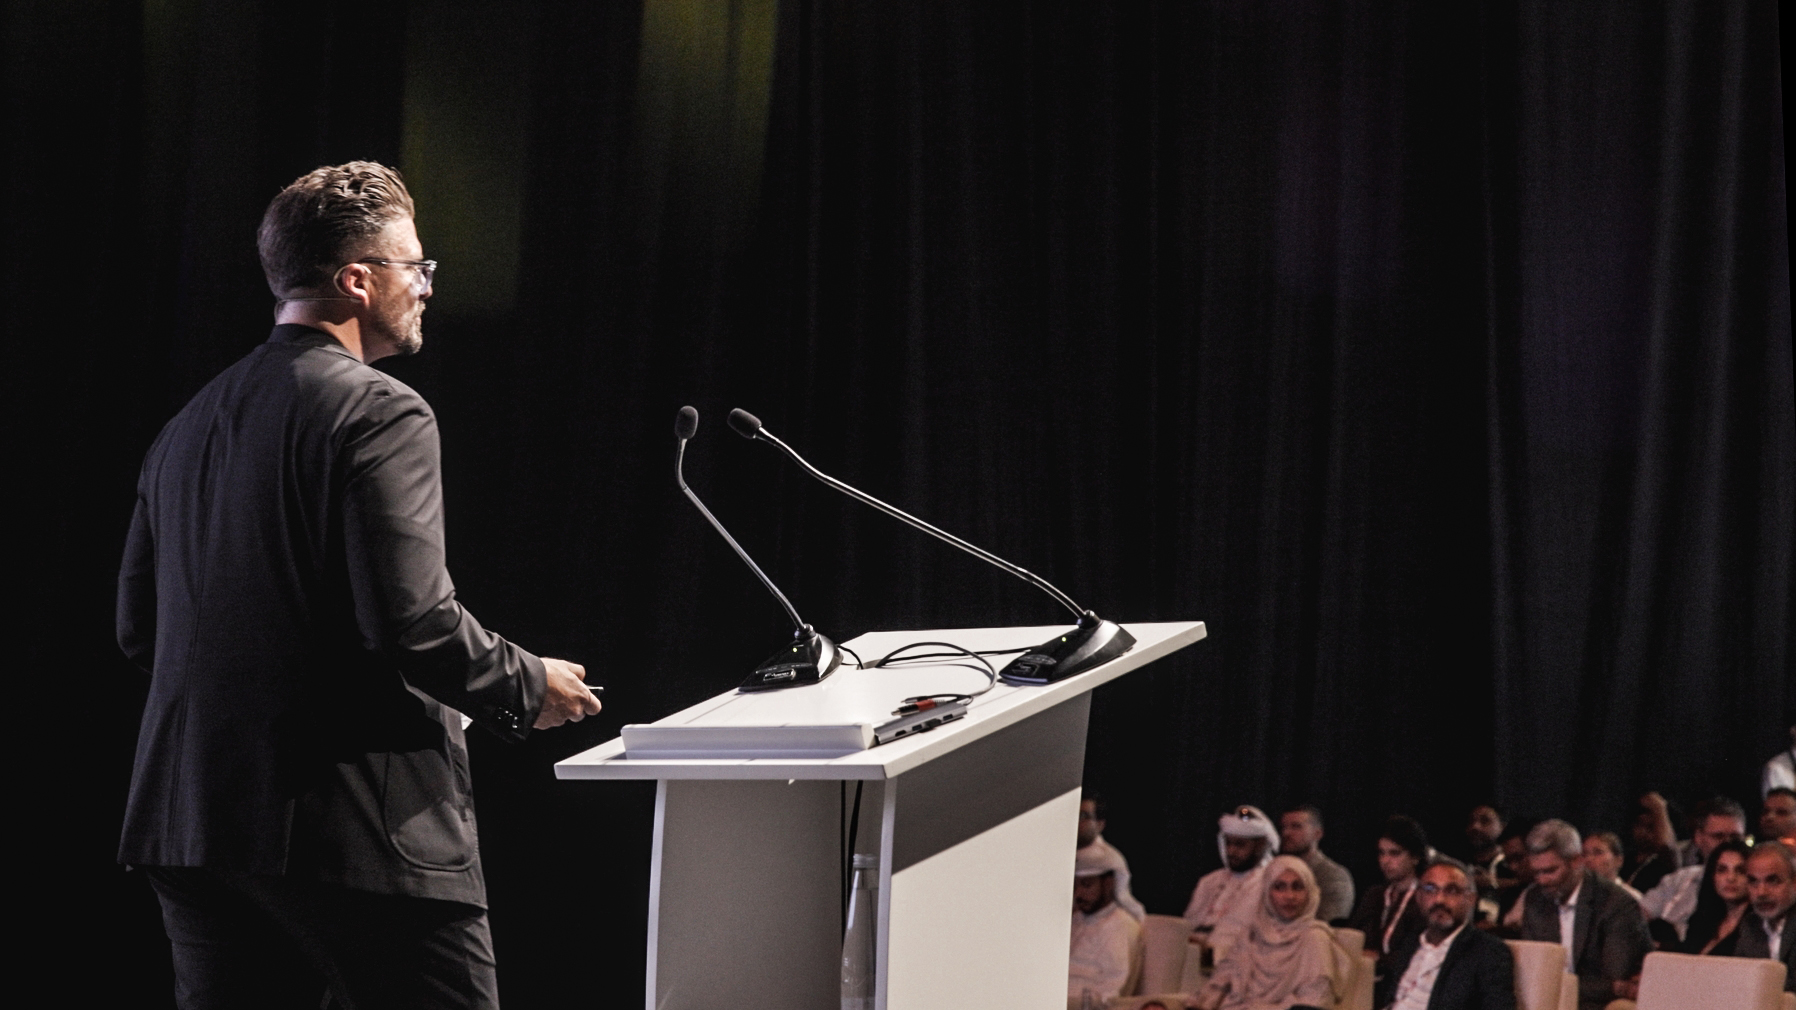
A highlight of the event was the keynote delivered by CEO and Co-Founder, Sandro Nafzger, on the GISEC main stage. His presentation explored why two or three annual pentests are no longer sufficient in an environment shaped by AI-powered threats and rapidly evolving technologies. Instead, organizations need an intelligent security testing program that learns and adjusts to changes in infrastructure, business context, and attacker behavior.
“What we need is the perfect symbiosis between artificial intelligence and human intelligence.”
Sandro Nafzger, CEO and Co-Founder, SignalFisher
While AI can help identify patterns and scale analysis, confidence ultimately comes from combining automation with expert human validation. This principle lies at the heart of SignalFisher's approach to intelligent security testing.
Confidence based on coverage, not assumptions
The discussions at GISEC also highlighted a broader market shift. Organizations are increasingly looking beyond vulnerability lists and isolated findings. They want assurance that their security program remains aligned with current risks and continuously validates what attackers can reach today. In other words, they wan’t peace of mind. Not confidence based on assumptions, but confidence based on coverage.
GISEC Global 2026 reinforced SignalFisher’s belief that security testing is evolving from periodic technical capabilities into a strategic business critical function. The future belongs to intelligent testing programs that never stop learning or adapting to changing environments, emerging threats, and organizational priorities.
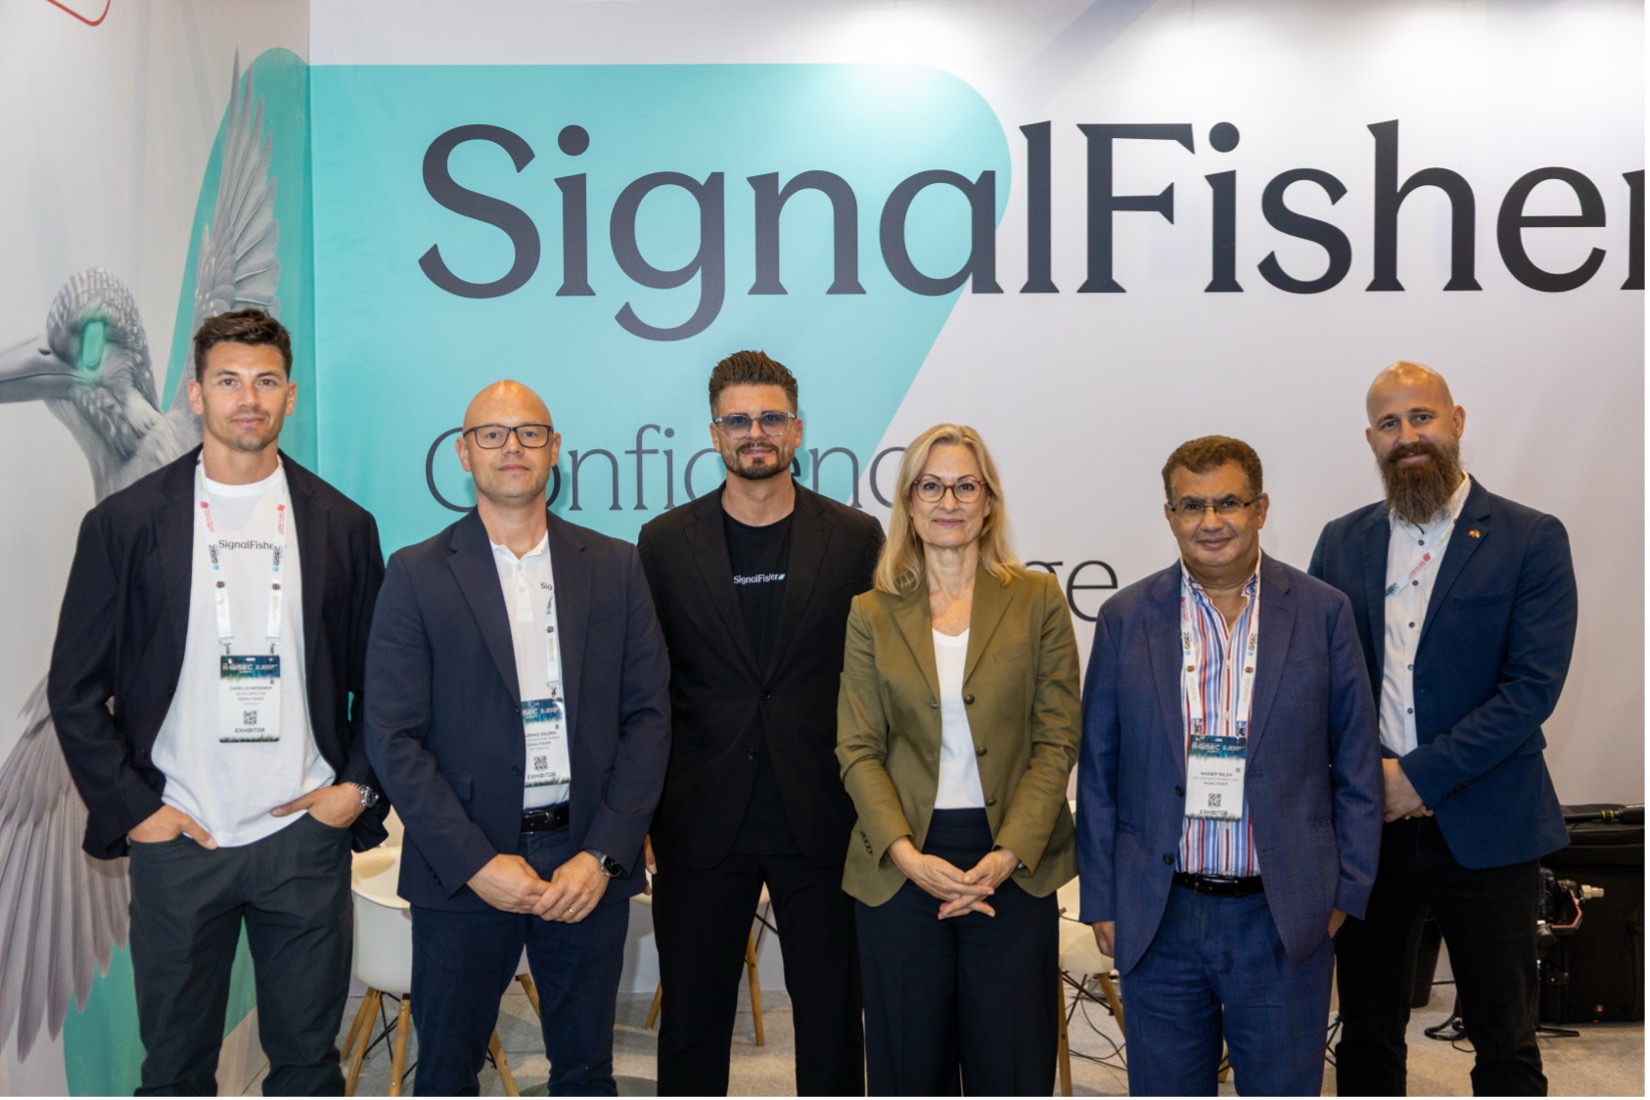
The team would like to thank everyone who visited the SignalFisher booth, attended Sandro’s keynote, and shared their perspectives throughout the event. The openness of the cyber security community and the quality of the conversations made GISEC 2026 an exceptional experience for the entire company.
CONFIDENCE FROM COVERAGE.
A security testing program that never stops learning. Relevant, current, and trusted.
Aftermovie: