

The Four Dimensions of Coverage – SignalFisher’s Approach
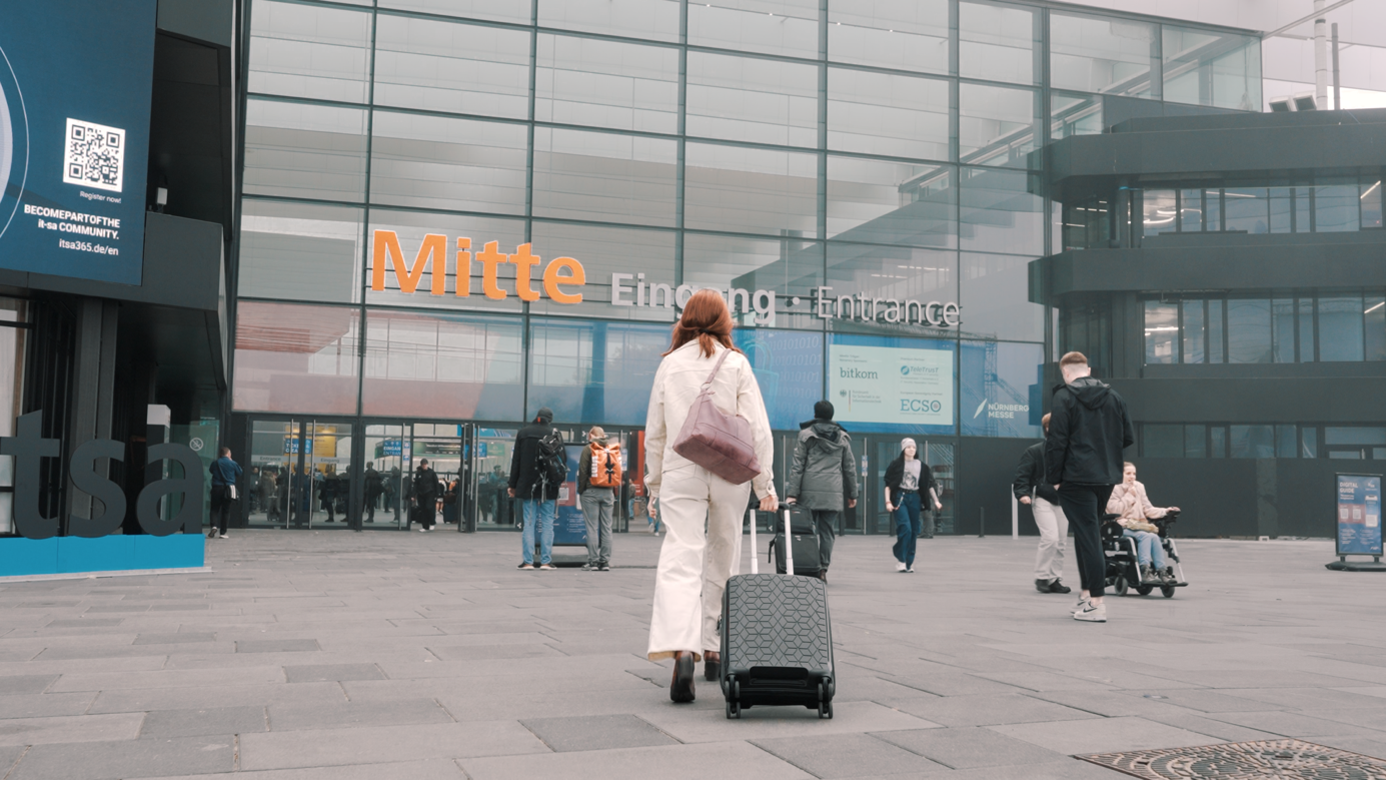
4 min. read – SignalFisher took the stage at it-sa Expo&Congress 2026. CEO and Co-Founder, Sandro Nafzger, used his platform to make a clear case. If you are only measuring security testing by the number of vulnerabilities found, your focus is too narrow. You are focused on exposure. What really matters is how well your entire ecosystem is covered, and there are four dimensions to consider.
Check the Barrier, Not the Water Level
Sandro opened his keynote with a metaphor comparing a water defense barrier and cybersecurity. His message, "If you only count the number of vulnerabilities found, you are essentially just measuring the rising water level." He argued it makes far more sense to assess how strong the water barrier is at keeping disaster at bay. The guiding question is no longer, “How vulnerable are we?” The focus should now be, “How well are we covered?” What has been tested, what has not, and how well is the business covered? Sandro’s case for security testing: Coverage is knowledge, and knowledge is power.

Think of Coverage Like Applying Sunscreen
Over the last decade, security testing has mostly been measured by surface exposure, and usually whether all relevant systems are in scope. Surface exposure certainly matters, but it is only one of four dimensions. To illustrate his point, Sandro reached for a summertime example. “When you put on sunscreen, it’s not just about making sure you haven’t missed a spot. It also matters how much you apply, and whether how strong the SPF strength is. Other considerations include things like how a small child needs a different sunscreen than someone who spends the whole day in the water. Lastly, one must consider how often to reapply. The best sunscreen, perfectly applied, is useless if you only put it on once a week.”
Security testing works the same way. Is everything relevant to the business in scope? This is surface coverage. Are we testing these assets often enough? This is temporal coverage. Have they been tested against the appropriate attack scenarios? This is scenario coverage. And how thoroughly were they tested? This is depth coverage. Only when all four dimensions have been taken into consideration can we capture an accurate reading of our security coverage. Only then do we have the ability to create a comprehensive testing program that continuously learns and adapts to the changing environment of our organizations. Sandro argues this information is worth far more than simply knowing that there are too many vulnerabilities to fix them all.

A Situational Picture the Board Can Understand
Viewed across all four dimensions, a large ecosystem of fragmented testing methods and systems becomes one cohesive picture from a bird’s eye point of view. This type of testing strategy shows the security engineers where to focus their efforts, management where to allocate resources, and the board where to focus company strategy.
There is no question that cybersecurity has been at the top of management’s concern for many years. The question today is how to close the widening gap between the number of vulnerabilities and limited resources available to patch. SignalFisher's focus is on closing that gap with an intelligent security testing program that adapts and learns with your business context, emerging threats, and the regulatory landscape. For Sandro, the answer lies in exactly this kind of signal focused triage. Ideally, you know how well every system and asset is covered, the last time each was tested, which assets have not been tested, and where more focused assessments are happening with experienced researchers.

From Individual Testing to an Intelligent Security Testing Program
This is where Sandro introduced SignalFisher’s platform. “We have built an end-to-end intelligent security testing platform, because the testing itself is only part of the work. Vital pieces to your security testing often start before testing begins... when it comes to understanding the context, developing a testing strategy, and adapting scope to the current circumstances. Another essential piece of the puzzle is when the testing results come in. These need to be translated so that everyone, from engineers to the board, knows where things stand and where the organization needs to focus."
He further stated, "SignalFisher coordinates with your IT security team’s existing testing methods and utilizes our network of expert security researchers to monitor and test your network from all four dimensions of coverage. It’s a program that works like a live stream, where your ecosystem comes together in one overall picture. The goal is to move from snapshots to a live testing environment that can be assessed in real-time. One that’s effective and efficient."
A Clear Answer to the Question That Matters Most
In the end, it all comes down to one question that every security leader will be asked sooner or later, “Where do we stand today? Are we covered?” Sandro wants every security leader from engineers to CISOs to be able to answer with evidence, “Yes. This is where we are covered. This is where we are not; and here is where we are focusing our efforts.” That is precisely what SignalFisher means by Confidence from Coverage.
Keynote video (in German):
About the author